Didier Stevens

Sunday 10 August 2008

Sampling a Malicious Site

Filed under: Malware,My Software — Didier Stevens @ 21:59

Fake CNN alerts galore!

I seize the opportunity to publish a new video (warning: 8 minutes of command-line staring) (hires XviD version here) showing you how to use my tools to retrieve malware samples hosted on a website. If you just visit an infected website with Internet Explorer, you run the risk of infecting your machine. The safe way to retrieve samples is to work in a low-risk environment (e.g. non-root account on a Linux VM) and use tools that are unlikely to be the target of exploits hosted on said website.

The following tools are featured in the video:

The file numbering trick (01., 02., 03., …) allows me to document exactly how I obtained the sample.

Since I recorded the video, the malware seems to have been removed from the site. But be careful, it’s not uncommon that compromised websites get reinfected.

Friday 8 August 2008

Fake CNN Custom Alert

Filed under: Malware — Didier Stevens @ 8:33

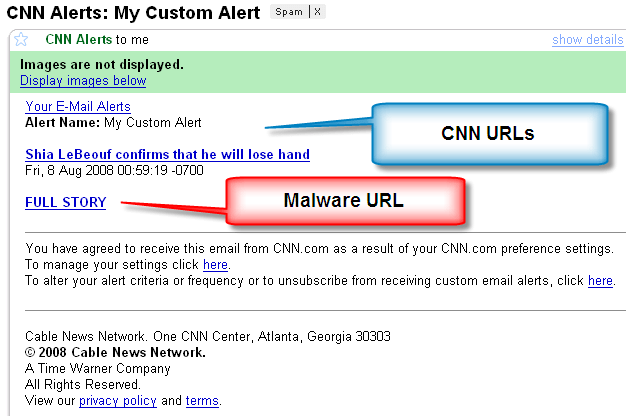
Here’s a new social engineering trick I hadn’t seen in my spam mail before:

The Shia link actually points to a real CNN article about the olympics & terrorism. So you might be inclined to click on the full story link.

Like the CNN Top 10 malware, it has a fake Flash update:

Which happens to be malware.

Thursday 7 August 2008

Update: USBVirusScan 1.7.2

Filed under: My Software,Update — Didier Stevens @ 8:40

I release USBVirusScan version 1.7.2.

Two new features:
-s scan available removable drives when USBVirusScan is started
-r also start the command at drive removal, parameter %e indicates drive arrival ‘A’ or drive removal ‘R’

Download:

USBVirusScan_V1_7_2.zip (https)

MD5: BDEF7BAE13C10B2B6CD650A89FD910ED

SHA256: 0090C73D6A3725E75C3388387A7A9E869C5D6BEA83E0D4D612E1CB25458163F3

Tuesday 5 August 2008

How Is My Hacking? (.com)

Filed under: Announcement,Nonsense,Puzzle — Didier Stevens @ 17:50

My new stickers arrived today:

From now on, winners of my little puzzles can expect a little prize (I’ll contact winners of past puzzles)…

Monday 4 August 2008

Update: wsrtool

Filed under: My Software,Update,WiFi — Didier Stevens @ 6:54

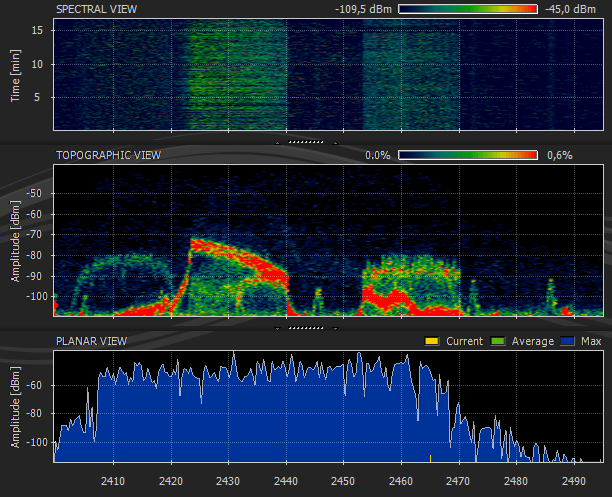
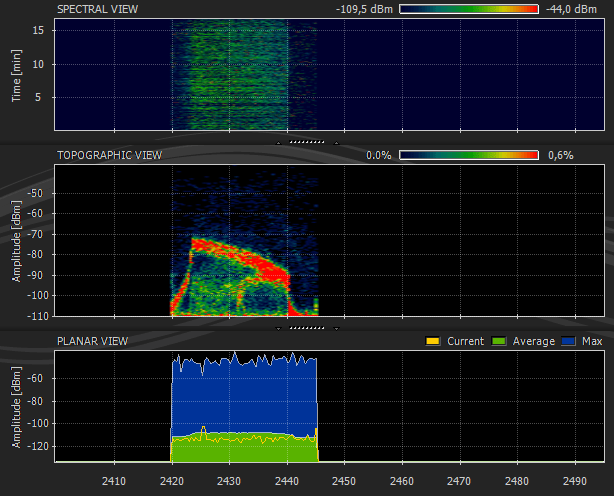
Ryan Goodings suggested I modify the header (starting_frequency and readings_per_sweep) of a band-pass filtered wsr file, to have Chanalyzer scale the filtered section. Here is the new version (use option –reduce), and this is the result:

Friday 1 August 2008

wsrtool

Filed under: My Software,WiFi — Didier Stevens @ 9:31

Another WiFi program: wsrtool.py This Python program allows you to process wsr files (capture files of the ISM spectrum, created by Chanalyzer with a Wi-Spy adapter).
The tool filters out selected frequencies or amplitudes (band-pass and band-stop filter).

You need to install the Python module Construct.

Here’s an unfiltered capture:

And here I used a band-pass filter with cutoff frequencies 2420 MHz and 2445 MHz:

Thursday 31 July 2008

F-Secure Reverse Engineering Challenge 2008

Filed under: Reverse Engineering — Didier Stevens @ 13:41

It’s back: http://www.khallenge.com.

And here’s a promo video I made last year.

Tuesday 22 July 2008

Authenticode Challenge

Filed under: Puzzle — Didier Stevens @ 21:03

Here’s a new puzzle, and “by popular demand”, it’s a couple of magnitudes harder than previous puzzles.

The puzzle is a Windows console application, you can download it here. When you run the program, it prints “Authenticode Challenge version 1” to stdin. The challenge is twofold:

1) make the program print “Authenticode Challenge version 2” (that’s easy)

2) update the digital signature to keep it valid (not so easy)

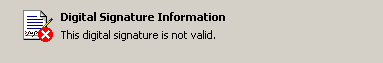
When you check the digital signature of the puzzle, you’ll see this:


And after you changed the program to print “Authenticode Challenge version 2”, you’ll see an invalid signature:

The challenge is to keep the signature valid, using a certificate with the same public key.

All the data you need from me is in the executable. You’re not allowed to hack my servers in search of the private key.

FYI: this puzzle was reviewed by a PKI expert, who confirmed the solution.

Good luck, I hope there will be many challengers, and better yet, with another solution than mine!

Monday 14 July 2008

A New Version of WhoAmI? and Another Little Puzzle

Filed under: My Software,Update — Didier Stevens @ 0:57

I’ve updated my WhoAmI? Firefox add-on for version 3.

You can download it here or get it from the Mozilla site. It has remained in the Sandbox since my first post, but now I’ve nominated to leave the Sandbox. If you use it, please post a review on the Mozilla page to help it on its way out of the the Sandbox (or keep it there if it’s too buggy).

And now for the little puzzle: what is special about this other version of my WhoAmI? add-on?

So don’t get confused by these 2 versions:

  • The real version of WhoAmI? is here
  • Download this other version only if you’re interested in a little puzzle

Saturday 12 July 2008

Infectee or Infector?

Filed under: Malware — Didier Stevens @ 10:32

My first and second little poll lead up to this post.

I’ve been quite surprised that the most downloaded file from my site is SafeBoot.zip. Since I published it more than a year ago, there have been 20,000+ downloads. And I’m also under the impression that the number of downloads per day is steadily increasing. One would be tempted to conclude from this that the number of malware infections that disable Safe Mode is on the rise, but this is indirect evidence.

First of all, I believe the increase is due to search engines. As more and more sites link to the Safeboot blogpost, the page will rise in the ranking of search results. One can argue that visiting the Safeboot blogpost and downloading the SafeBoot.zip file are two different things: you can land on the page just out of curiosity, but if you download the registry fix file, then you’re surely infected with a Safe Mode disabling virus.

Well, not necessarily. From my interactions with people using my registry fix, I’ve observed that some of them apply this fix even if their Safe Mode keys are intact. They just have another PC problem (for example the CD drive doesn’t work anymore), and they hope that my fix will fix this too.

So I’m not sure that Safe Mode disabling malware is on the rise, but I do know that it’s becoming more sophisticated. As the first virus I analyzed would only delete the Safe Mode keys once, now there are viruses that delete the Safe Mode keys and monitor them, deleting them again if they are restored.

Ironically, another large group of people that visit my site are not in search of a solution to a malware infection, but are looking for malware! Here are some of the most popular search terms that lead to my blog:

  • download virus
  • virus download
  • download a virus
  • how to get a virus
  • get a virus
  • give me a virus

The reason that search engines direct users to my site when they search for a virus, is an unfortunate side-effect of my Google Adwords post. This is my most popular blogpost by far, and has been linked to by countless sites. Although I have offer no malware to download, this Adwords blogpost contains the words of the search terms and is highly referred to, so it ranks high in search engine results.

So if you’re landing on my blog via a search engine, it’s very likely you’re an infectee or an infector. 😉
« Previous Page — Next Page »

Blog at WordPress.com.