Didier Stevens

Sunday 15 March 2020

pecheck.py Version 0.7.10

Filed under: My Software,Update — Didier Stevens @ 9:12

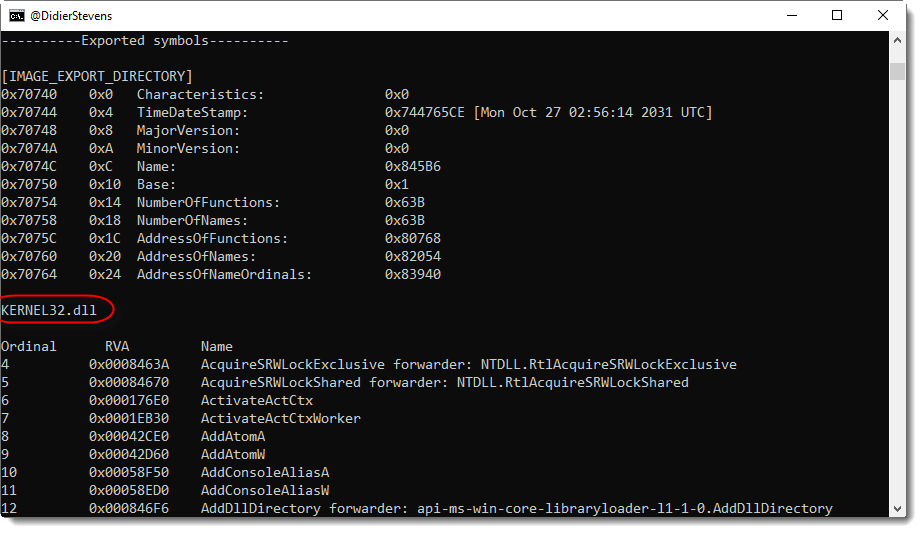
In this new version of pecheck.py, a tool to analyze PE files, overlay offset calculations are improved when a digital signature is present, and the output has changed slightly:

  1. the name of the export DLL is included (right before the list of exported functions)
  2. lists of relocation addresses are dropped
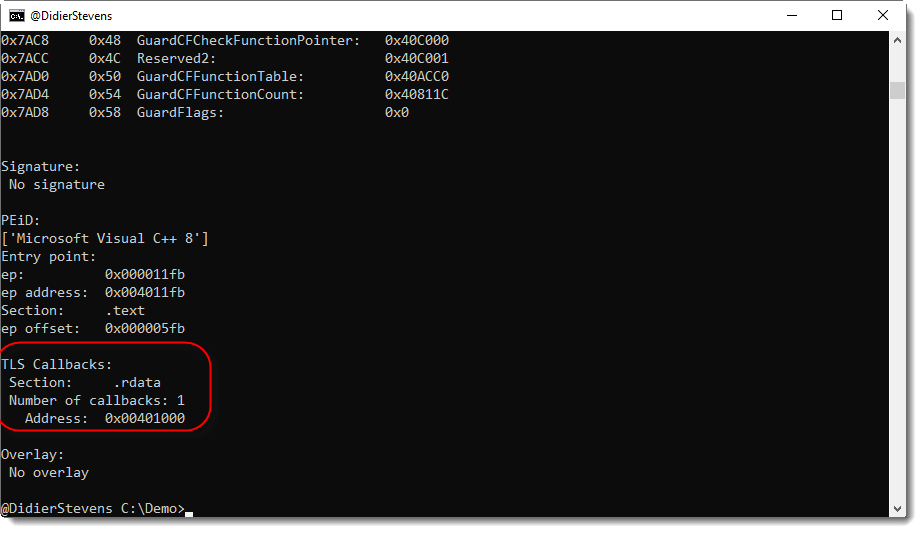
  3. TLS callbacks are reported

No TLS data:
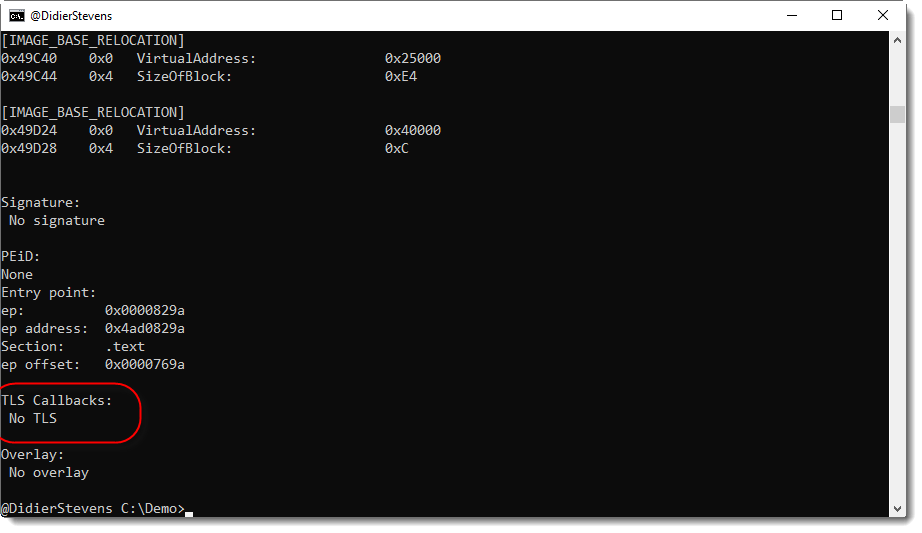
TLS data present, but no callbacks:

One TLS callback:
pecheck-v0_7_10.zip (https)
MD5: D0C4332B1BD231AA131FBCDCD3BBBA33
SHA256: 0E57A50590D59321CCD0BECE0936CF9523668F86516F56F5B2A21B9DCA9B4788

Saturday 14 March 2020

Update: cmd.dll Version 0.0.5

Filed under: My Software,Update — Didier Stevens @ 15:24

I noticed that I didn’t post the latest version of my cmd.dll program.

And I looked into moving this code to the new ReactOS builder, but that still does not offer 64-bit builds, thus I’m postponing this migration.

cmd-dll_v0_0_5.zip (https)
MD5: 9BDBB368CDB576BDC05DDE76BC30702F
SHA256: 4757333DD509C77504E3FFCD1B01A2FFC6EC80AE518AE9CD787E80BF1281806D

Tuesday 10 March 2020

Update: oledump.py Version 0.0.48

Filed under: My Software,Update — Didier Stevens @ 0:00

This new version of oledump.py brings an update to plugin_biff (improved formula parsing) and fixes for Python 3.


oledump_V0_0_48.zip (https)
MD5: B869EC84DB4F10596212A2B67CF2C684
SHA256: 0E66E3EA42D5761301E0643A27D892B3C4531CCC2E4C95373ECE9B7AD7E6DAC6

Sunday 8 March 2020

Update: oledump.py Version 0.0.47

Filed under: My Software,Update — Didier Stevens @ 22:22

This new version of oledump.py brings Root Entry listing with option –storages and %CLDISDESC% extra parameter.

plugin_biff.py is updated to be faster and has new options -X and -d (pure hexadecimal dump and binary dump).

plugin_clsid.py is a new plugin.

More details in coming blog posts and ISC diary entries.


oledump_V0_0_47.zip (https)
MD5: E851ED7240C08E9E9E3EBA4A412A46A4
SHA256: F35997537D5C4596E413D08C35A83EBD55CAF587D2D9898DAA9285BC83CAF287

Sunday 23 February 2020

Update: Python Templates Version 0.0.2

Filed under: My Software,Update — Didier Stevens @ 0:00

Here is an update to my Python templates (binary and text files).

I’ll explain the updates to each template in upcoming blog posts.

python-templates_V0_0_2.zip (https)
MD5: 082812485D24AD0E3D12F1618BC44367
SHA256: 98DE8BEC508C7E678D294DD630466DA175524D4180C1E8C3A6C06EE11587981E

Saturday 22 February 2020

Update: translate.py Version 0.2.7

Filed under: My Software,Update — Didier Stevens @ 20:29

This update for translate.py, a tool to “Translate bytes according to a Python expression”, adds a new function for XOR multy-byte-key encoding/decoding.

translate_v2_5_7.zip (https)
MD5: 886C1B4C518EA58F972F87980994B976
SHA256: 01E4239E050DE4853AC53020CCE44C9804003A4A2C195974B5B16AEDD1B8E1B1

Monday 17 February 2020

Update: format-bytes.py Version 0.0.13

Filed under: My Software,Update — Didier Stevens @ 0:00

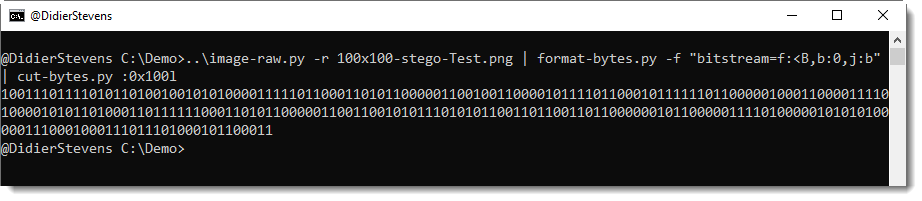
This new version of format-bytes.py brings a new option when extracting bitstreams: producing a stream of 0s & 1s, like this:

Join specifier j:b (option “-f bitstream=…”) produces a bitstream of 0s & 1s, that I can then process further:

The png file I analyze in this example, was created with PHP Stegger on the Geocaching Toolbox site.

format-bytes_V0_0_13.zip (https)
MD5: E7A7A344B3B8753553FC5B2E4084D8DA
SHA256: 1F22A1D784DCF1269FFD12E2C9467EE0FB93B0895CC24D04CBBD9696D50945DB

Sunday 16 February 2020

Update: hex-to-bin.py Version 0.0.4

Filed under: My Software,Update — Didier Stevens @ 0:00

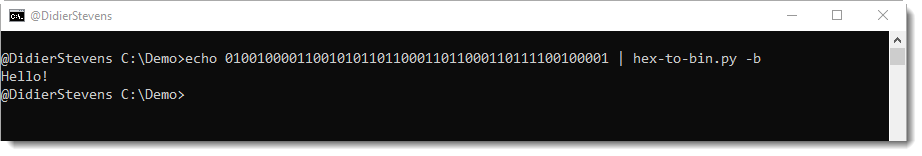
This version of hex-to-bin.py, a simple tool to convert hexadecimal data to binary, can also handle bitstreams (option -b) with this update. If necessary, the bitstream is right-padded with 0s to make the bitstream length a multiple of 8.

Example:

hex-to-bin_V0_0_4.zip (https)
MD5: CBD3D27A2BC703F51FB23F757084BBE1
SHA256: CD70D7644BB353C64DD37AA0717B14967176A1A5E35E5DC6AE163D929BE13AAD

Tuesday 11 February 2020

Update: xmldump.py Version 0.0.4

Filed under: My Software,Update — Didier Stevens @ 0:00

This new version of xmldump.py, a tool to parse and display xml content, has a new command: pretty.

As its name implies, this command performs a pretty print of the xml content.

xmldump_V0_0_4.zip (https)
MD5: A97F4048226BD9A0BE47D1ABDEC5D770
SHA256: 2636D10294C5BCD8B1E97DFE30745FF91496FB9F87ABB8D99371B379AA711B25

Monday 10 February 2020

Update: oledump.py Version 0.0.45

Filed under: maldoc,My Software,Update — Didier Stevens @ 0:00

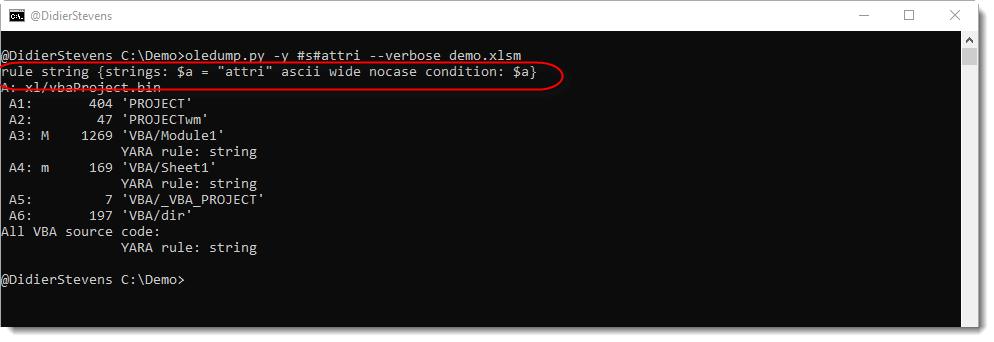
This new version of oledump.py has a feature to display Ad Hoc YARA rules using option –verbose.

In this example, I show a string Ad Hoc YARA rule to search for string attri (-y #s#attri). By including option –verbose, the YARA rule generated by oledump for string attri is displayed first:

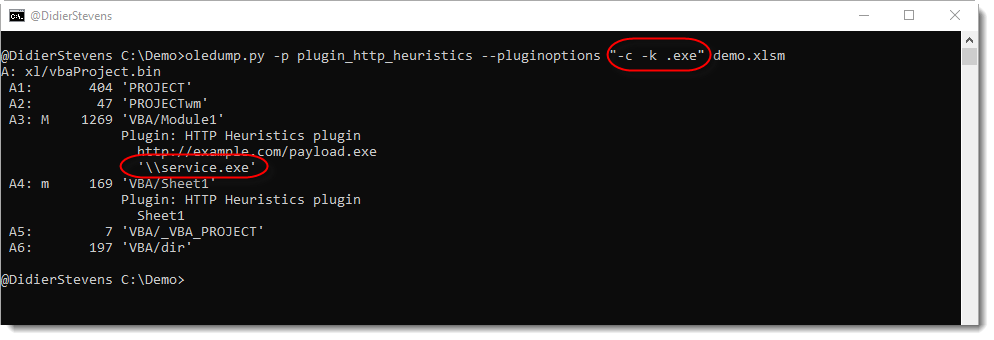
Plugin plugin_http_heuristics has a new option: -c –contains.

By default, plugin_http_heuristics looks for (obfuscated) strings that start with keywords (http:// and https:// by default). Option -c changes this behavior: when this option is used, the keywords are searched in the entire string, and not just at the start.

In this example, I use this feature to search for the filename of the dropped executable (strings containing “.exe”):

And I also include plugin_vba: this is an old plugin that I failed to release. It searches for string concatenation in VBA code.

Video:

oledump_V0_0_45.zip (https)
MD5: FB9694358CCEAE4AFDFCF97FDA0D5205
SHA256: FB75B1E19E5067751E2DE1AD21826245B7E11EDBE03278566484754F606F3965

« Previous Page — Next Page »

Blog at WordPress.com.