I’m doing my White Hat Shellcode workshop at Hack.lu 2012.

I founded my own company: Didier Stevens Labs

You can find videos of my workshops for sale on this new website.
And I will give a brand new workshop at Brucon next week: Windows x64: The Essentials
I will sell CDs with my workshops videos at Brucon with a 20% discount.
I’ve worked on a couple of new tools to analyze the digital signature found in PE files. In this post, I’m sharing some invalid signatures I found on my machines.
This signature is invalid because the certificate expired:
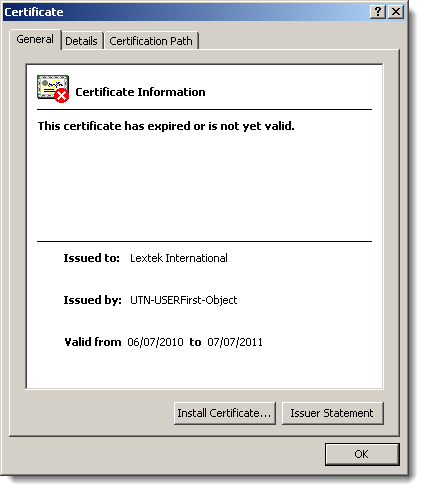
Normally, the fact that it expired shouldn’t cause the signature to become invalid, but here it does because the author forgot to countersign the signature with a timestamping service:

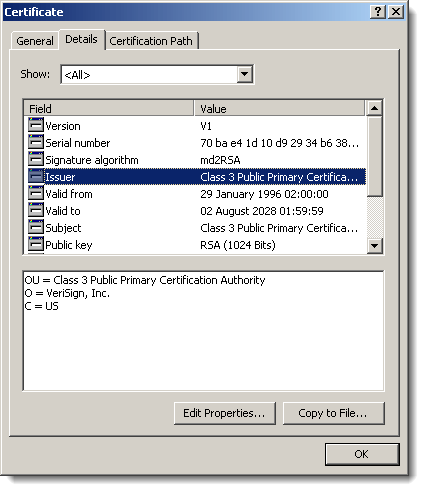
I also found several files where the root certificate used in the signatures uses a signature algorithm based on the MD2 hash:
And last a signature with a revoked certificate:

Remember Realtek Semiconductor? Their private key was compromised and used to sign Stuxnet components.
The latest (IN)SECURE Magazine issue includes my article on White Hat Shellcode.
Do you need to analyze a Cisco IOS Core Dump?
Read this.
“But that doesn’t explain how to analyze a core dump“, you say? Correct, unfortunately. That’s all you get with SOPA/PIPA enacted.
“But SOPA blackout day” was yesterday, you say? Correct. But I’m not following the crowd 😉
Hakin9 has published my bpmtk article. The article mentions bpmtk version 0.1.4.0; however, this new version has no new features. But it comes with extra PoC code, like a LUA-mode keylogger and “rootkit”. New blogposts will explain this new PoC code.

And upcoming bpmtk version 0.1.5.0 contains a new feature to inject shellcode. Just have to update the documentation.
On the PDF front: I’ve produced my first Ruby code ;-). I worked together with MC from Metasploit to optimize the PDF generation code in this util.printf exploit module. It uses some obfuscation techniques I described 8 months ago.
My new stickers arrived today:

From now on, winners of my little puzzles can expect a little prize (I’ll contact winners of past puzzles)…
I’ve a blogpost over at the PaulDotCom Community Blog about my GSSP-C certification.
From now on, I’ll intersperse my blog with Quickposts.
I’ve a need to post short tips and tricks, mainly for my own reference. These Quickposts will document solutions for small problems I encountered during my work or research. I could also use a Quickpost to announce a discovery I don’t plan to research extensively.
The main characteristic of Quickposts will be the limited amount of time and research I spend on them, hence the quality of the content will suffer.
Quickposts have their own Quickpost category, the title will always start with Quickpost:, and if a Quickpost requires updating (to correct errors), I will edit the post instead of publishing a new Quickpost.
The first Quickpost will be about installing Kismet on my N800.
Of course, I stay committed to my weekly posts.