This new version of oledump.py comes with Excel 4 formula parsing improvements in the plugin_biff plugin.
oledump_V0_0_61.zip (https)MD5: 6DC34FFAF4ED0066696ED230878AEED9
SHA256: 41A68ABA19BBA74DAE653BE62D4A63A5AE409FB6DC1DAEEB2D419AA1B493728A
This new version of oledump.py comes with Excel 4 formula parsing improvements in the plugin_biff plugin.
oledump_V0_0_61.zip (https)There are no code changes to this version of 1768.py, my tool to analyze Cobalt Strike beacons.
What is new, is file 1768.json: this file contains statistical data for license IDs.

Over a period of one month, I collected license ID information from these sources: threatviewio and @cobaltstrikebot.
For each license ID that is found on more than one IP address / hostname, I include simple statistics: the number of unique IP addresses / hostnames and the number of unique public keys.
When analyzing malicious Cobalt Strike beacons, I often see recurring license IDs. That’s why I decided to add logic and a JSON file to my tool, with license IDs I’ve seen before. And now this has evolved to a small repository of often seen license IDs.
Here is an example with a sample we discussed on the Internet Storm Center diary:

The license ID is 1873433027 and this ID is associated with 18 unique IP addresses / hostnames, and 15 unique public keys. This is a clear indication that this license ID is used by malicious actors. License IDs that have been seen only once, could belong to red teams, that is why they are not included in file 1768.json. The more often a license ID is seen, the higher the chance it is used by malicious actors. Of course, it is not excluded that there are legitimate license IDs from red teams in this list, but I expect they will have low frequencies.
Takeaway: if your sample has a license ID that appears in 1768.json, then it has been seen before (at least twice), and you’re likely not dealing with a pentest.
1768_v0_0_7.zip (https)Here is an update to my Python templates.
I use these templates as a starting point for new tools or for quick development of ad-hoc tools.
I also recorded a video showing how to use my template to create your own tool: ssdeep Python Example Based On My Templates.
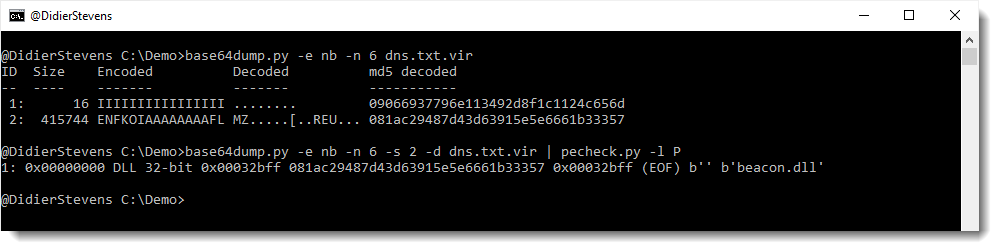
python-templates_V0_0_5.zip (https)This new version of base64dump.py supports a new encoding: NETBIOS Name encoding.
NETBIOS Name encoding is very similar to hexadecimal encoding: in stead of hexadecimal digits 0-9 and a-f, letters A-P are used.
I encountered this in DNS TXT records of a Cobalt Strike DNS stager. More on that later.
This new version of re-search.py adds gzip support and filtering of private IPv4 addresses:

This new version of 1768.py, my tool to analyze Cobalt Stike beacons, has fixes, support for more encodings, and an option to output the config in JSON format.
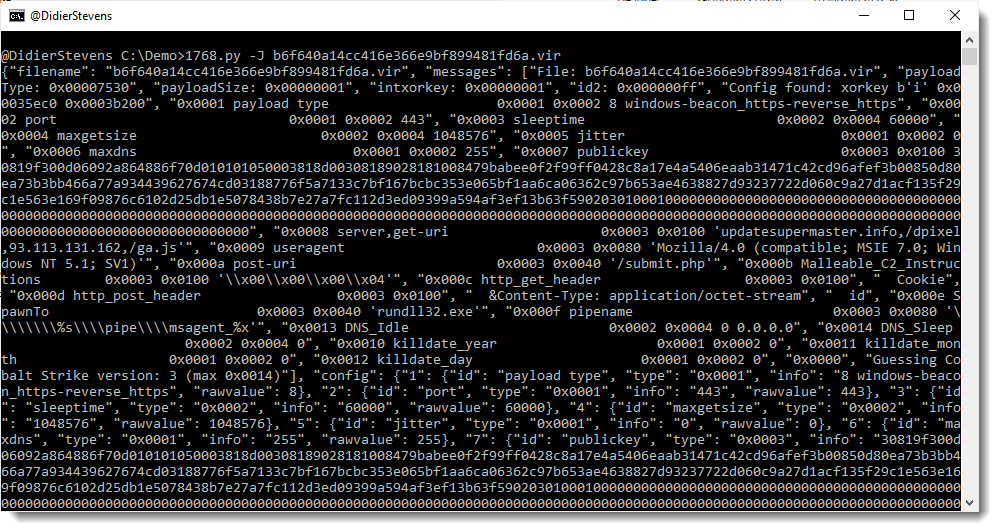
I updated the analysis logic in this new version of my tool 1768.py to analyze Cobalt Strike beacons.
There’s a new option -c (–csv) to output the config values in CSV format.
And now with option -r (–raw), identical configs are de-duplicated.
1768_v0_0_5.zip (https)
MD5: 83D7A867B93FAC13BA24F17DDA994A9A
SHA256: CBCB84B9C4D8C1ED05983C2A211E3EA6029E69782FDDD6E15181EE4F47383EB5
This new version of pecheck.py, my tool to analyze PE files, outputs the hash of the embedded Authenticode signature.
pecheck-v0_7_13.zip (https)
MD5: 5B5179FFBE7530AA60C7182B830B54AB
SHA256: 4CFAF98CC8F3B06E3BBD7D6F37040B47641C38E49BD2975165FB328D50D3F08C
I use my tool nsrl.py to match a list of hashes with the Reference Data Set of the National Software Reference Library.
This is a Python 3 update and small change to support a change in RDS ZIP file structure.
nsrl_V0_0_3.zip (https)
MD5: A86E3EB076B467C64A520256556EDADA
SHA256: 8760B20A918CD135B7D79F7567C240AEF4840325BE9656D684BFD119A017E86F
This new version of oledump.py brings an update to plugin plugin_biff to help with the recovery of protection passwords.
oledump_V0_0_60.zip (https)
MD5: BC7631059077294223BB225D16FB7186
SHA256: D847E499CB84B034E08BCDDC61ADDADA39B90A5FA2E1ABA0756A05039C0D8BA2


